
Harden
Local endpoint security runtime that inspects and validates coding agent tool calls to stop destructive operations before execution.
Community:


Product Overview
What is Harden?
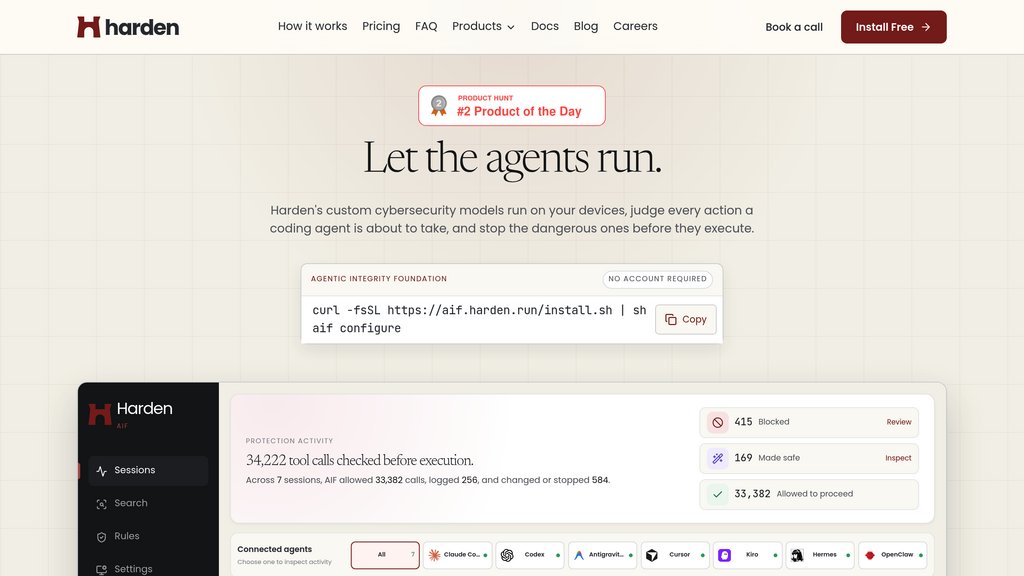
Harden (Agentic Integrity Foundation) is a specialized endpoint security guardrail designed to safeguard local workstations and cloud infrastructure from unintended autonomous agent actions. Operating custom cybersecurity models directly on developer devices, Harden inspects tool calls, terminal commands, and API requests before they execute. Unlike basic sandboxes or credential proxies, it actively evaluates intent and impact across supported tools like Claude Code, Cursor, and Codex, safely blocking catastrophic commands, steering agents toward safe retries, and maintaining fully local audit records.
Key Features
Pre-Execution Tool Interception
Inspects and evaluates terminal commands, cloud scripts, and agent tool calls in real time to prevent destructive actions before execution.
On-Device Security Engine
Runs proprietary cybersecurity models locally on developer machines without transmitting code, context, or private telemetry to external cloud servers.
Broad Agent Ecosystem Support
Integrates via native hooks and MCP proxy fallbacks across major coding agents, including Claude Code, Cursor, Codex, Kiro, Hermes, and OpenClaw.
Block-and-Steer Remediation
Safely halts hazardous commands like production deletions while supplying safe retry alternatives to keep agent workflows moving forward.
Local Decision Store
Maintains an unconstrained, local audit history of all allowed, modified, and blocked tool calls without mandatory account creation.
Use Cases
- Production Infrastructure Guardrails : Prevents coding agents from inadvertently deleting cloud namespaces, dropping remote databases, or running catastrophic deployment commands.
- Safe Autonomous Terminal Execution : Monitors shell commands during automated coding and refactoring sessions to halt dangerous file operations and privilege escalations.
- Credential and Data Leak Prevention : Stops agents from passing sensitive keys or proprietary code snippets into unauthorized external endpoints during task execution.
- Engineering Compliance and Auditing : Gives software teams verifiable, local activity logging and zero-telemetry security monitoring across autonomous developer workstations.
FAQs
Harden Alternatives

Convox
Unified platform for deploying, scaling, and managing cloud applications with streamlined DevOps workflows and robust security.

Zeet
Multi-cloud deployment platform that simplifies Kubernetes and infrastructure management with built-in CI/CD and developer-friendly tools.

Tensorfuse
Serverless GPU runtime enabling seamless deployment, fine-tuning, and autoscaling of AI models on private cloud infrastructure.

Codesphere
Developer-centric cloud platform enabling seamless deployment, autoscaling, and management of complex applications with minimal configuration.

ClawCloud Run
Cloud-native platform for rapid app deployment, management, and scaling with integrated GitOps workflows and native Docker/Kubernetes support.

OpenSauced Pizza
A command-line tool and GitHub Action that automates repository management and code ownership insights for open source projects.

UbiOps
A flexible platform for deploying, managing, and orchestrating AI and ML models across cloud, on-premise, and hybrid environments.

dstack
Open-source container orchestration platform tailored for AI workloads, enabling seamless GPU resource management across cloud and on-premises environments.